Overview
After some months of “break” (I was actually busy reversing an AV engine, I’ll write a blog post on that sooner or later) I decided it was time for me again to go back to the fascinating world of kernel (driver) exploitation. I’ll keep it short since I didn’t do any actual “research” around here but I just got curious around the mechanism of IObit Unlocker software which basically allows you (with kernel privileges, of course!) to unlock and remove any file you want.
I know what you’re thinking, this is not a security vulnerability since it does not cross any security boundary (it just go straight from admin to kernel) and I do not have any intention to find a vulnerability here (at the moment, but I will I promise). I just wanted to understand the underlying mechanism and reverse this driver just for the love of the game.
Introduction
The first thing you do when you gotta reverse a driver is to ask yourself which kind of driver you got in front of you. In this case, this driver gives a very powerful primitive since it allows any enough privileged user (admin) to delete any file and terminate any process and since kernel drivers usually run with ring-0 privileges well that means you can basically kill/terminate any process you want. Yes also protected ones like msmpeng.exe (MS Defender AV) or, as showed in my video-showcase eppwsc.exe (Emsisoft Anti-malware).
Let’s scratch the surface with IDA
One of the first thing you’re gonna find when you reverse this driver is to look at the import table and find the ZwTerminateProcess which resides at sub_140002ED4, in the same function there is a whitelist of processes that can’t be killed no matter what, IObitUnlocker is not allowed to kill the following processes:

Here you can see the fake IObitUnlocker.exe has not been killed:

Now that we know that IObitUnlocker is designed to delete any file and kill any process with Kernel-level privileges, we start from the sub_140002ED4 function (sink) and we press “x” every time to go back to the main function DriverEntry (source), or in this case we need just to arrive to the Dispatcher function, in order to understand which IOCTL is responsible for the invocation of ZwTerminateProcess (or you can just use some IDA Pro plugins that will tell you this information). After arriving to the dispatcher function DispatchDeviceControl we find out its IOCTL code is 0x222124:

So now we got all what we need to build a PoC that sends the IOCTL code 0x222124 and kills an arbitrary process. Yes I built the PoC with Claude Code, don’t judge me, you can find the full code PoC here: https://github.com/zer0matt/IObitUnlocker-Killer
Showcase
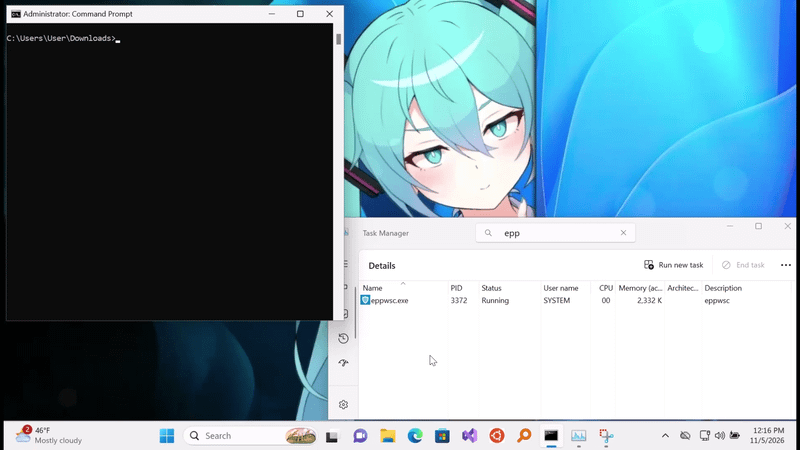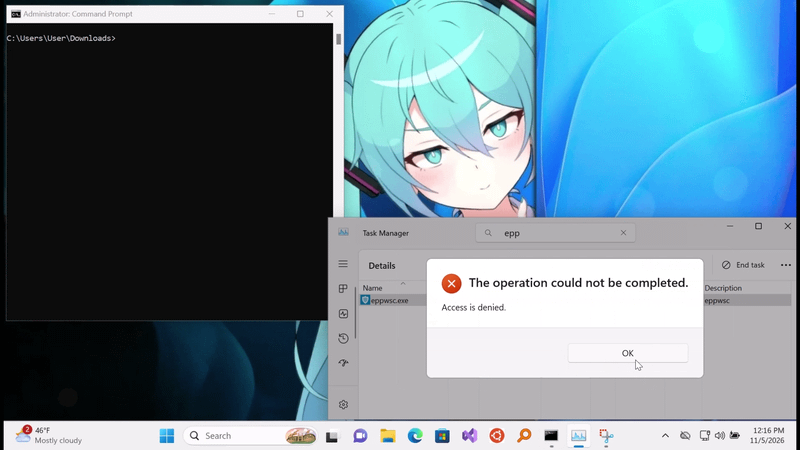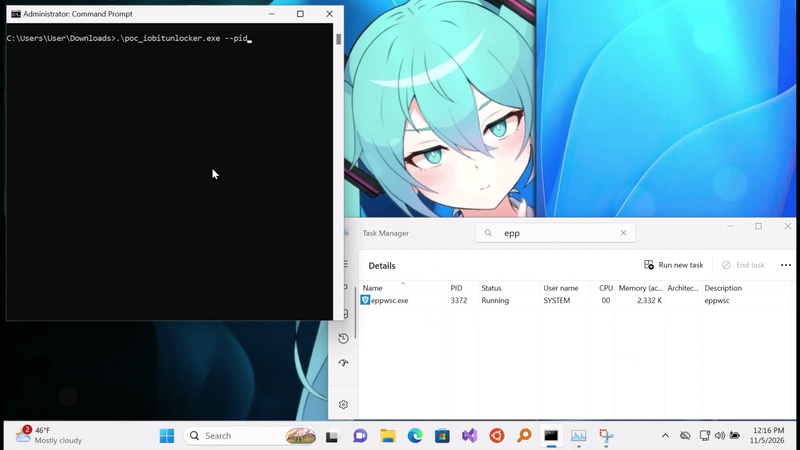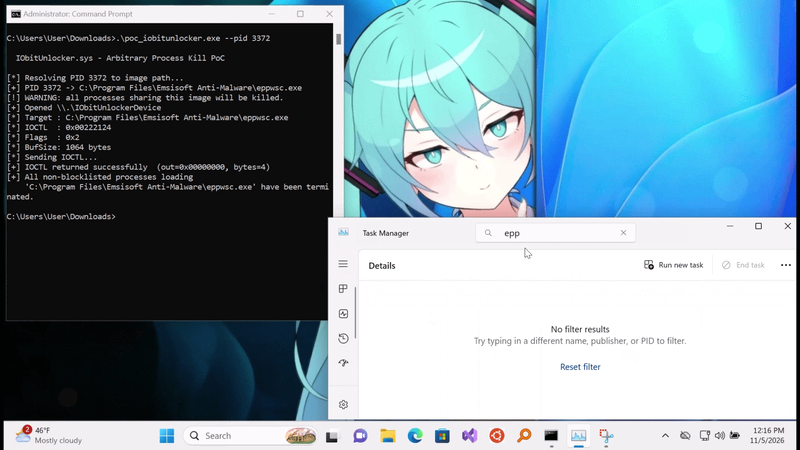
Conclusion
That was a brief demonstration on how powerful kernel drivers can be and how they can be weaponized by threat actors to kill AV/EDR processes and deploy malwares and ransomwares more easily. The best thing is that it is a correctly signed and valid driver so you can use it freely.


No comments:
Post a Comment